---
canonical: "https://www.jsolly.com/blog/admin-honeypot-page-to-catch-hackers/"
title: "Securing Your Django Admin Page With django-admin-honeypot"
description: "Protect a Django admin page from bots and hackers with django-admin-honeypot. Learn how to implement logging and email notifications of failed login attempts."
author: "John Solly"
published: "2022-05-08T15:15:49.000Z"
updated: "2026-09-07T14:25:05.471Z"
---
# Securing Your Django Admin Page With django-admin-honeypot
https://www.helpnetsecurity.com/2020/02/06/detecting-zero-day-iot-exploits/
I recently came across this python module, [django-admin-honeypot](https://duckduckgo.com/?q=django-admin-honeypot&t=osx&ia=web), and it's genius! The way django-admin-honeypot works is that it changes the /admin route to a fake login page and logs any login attempts in the database. See [my PR](https://github.com/jsolly/blogthedata/pull/39) for more details on the implementation.
Try logging into my admin page with whatever username/password you want.
https://blogthedata.com/admin
I store every login attempt in the database for later review. The username field tells me what username they tried to use (don't worry, I don't know what password you tried).
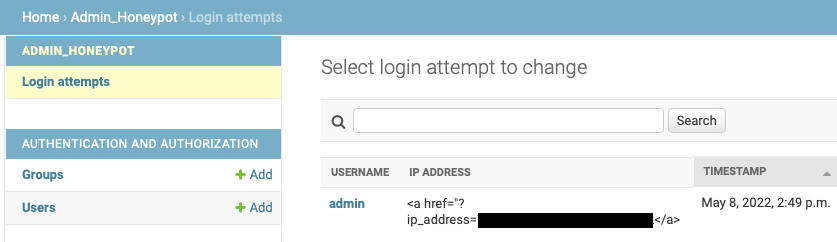
If I want to be extra hardcore, I could use a combination of the admin-honeypot signal hook and a tool like [fail2ban](https://github.com/fail2ban/fail2ban/wiki) to block any IP address that tries to login on this page (don't worry, I haven't implemented that, so hack away).
If you add this entry into your signals.py file, you can catch all login attempts to this page with the user's IP address as a local variable. I might add an email notification to my implementation so I get an email as soon as someone tries to login.
from admin_honeypot.signals import honeypot
@receiver(honeypot)
def my_callback(sender, **kwargs):
    print("Caught ya!")
    # send an email to the webmaster?
Haven't caught any hackers or bots yet, but was sure fun to implement!
May 8, 2022 in [Web Dev](https://www.jsolly.com/blog/category/web-dev/)
Updated September 7, 2026